 James Thompson
TL;DR: The UK's Product Security and Telecommunications Infrastructure (PSTI) Act 2022 — widely referred to as the Smart Devices Security Act — sets three mandatory security requirements for all consumer connectable products sold in the UK. Since 29 April 2024, manufacturers, importers, and distributors face fines of up to £10 million or 4% of global turnover for non-compliance. In 2026, the Office for Product Safety and Standards (OPSS) has ramped up enforcement activity, making compliance not just a legal necessity but a commercial priority. This guide explains what the Act demands, who is responsible, and how to achieve full compliance before regulators come knocking.
What the UK Smart Devices Security Act Actually Covers
The Product Security and Telecommunications Infrastructure (PSTI) Act 2022 is the legislative framework behind the UK's Smart Devices Security Act. Part 1 of the Act covers consumer connectable products — a category far broader than smartphones and laptops. Any device that connects to the internet, a mobile network, or another device by Wi-Fi, Bluetooth, or similar technology falls within scope.
Products covered include smart TVs, wireless speakers, security cameras, baby monitors, home routers, wearable fitness trackers, smart doorbells, and connected home appliances such as washing machines and thermostats. Notably, the Act does not cover laptops, desktop computers, medical devices regulated by the Medicines and Healthcare products Regulatory Agency (MHRA), smart meters, or electric vehicle charging points — each governed by separate regulatory regimes.
The Act applies to all three supply chain actors: manufacturers, importers, and distributors. A UK-based retailer that imports connected products from an overseas manufacturer carries independent legal obligations under the Act. Simply assuming the manufacturer has handled compliance is no longer legally defensible. Each actor has documented duties and must be able to demonstrate conformity on request from the OPSS.
Key principle: The PSTI Act adopts a "security by design" philosophy — security requirements must be built into products from inception, not bolted on after sale.
The Three Mandatory Security Requirements for Connected Products
The PSTI Act mandates three baseline security requirements, drawn from the internationally recognised ETSI EN 303 645 standard for consumer IoT. These requirements are not optional guidelines — they are minimum legal obligations.
1. No Universal Default Passwords
Every connected product sold in the UK must come with a unique password that differs from device to device. A password is considered "universal" if it is the same across a product range, or if the product can be reset to a universal factory default. Both are prohibited under the Act.
Acceptable implementations include: a unique password printed on the device or in its documentation, a password generated randomly at first use, or a mandatory setup process that requires the user to create a password before the device can operate. Passwords following predictable patterns derived from device serial numbers or MAC addresses are also prohibited — the regulation targets guessability, not just universality.
2. Vulnerability Disclosure Policy: What Manufacturers Must Publish
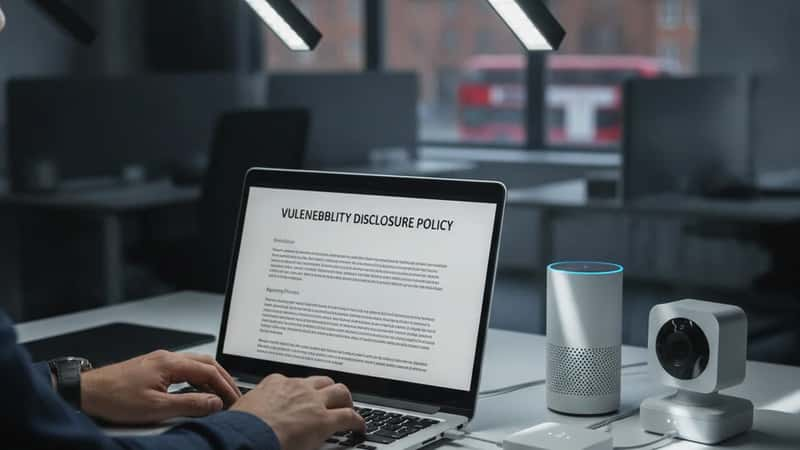
Manufacturers must maintain a publicly accessible vulnerability disclosure policy. This is not a private internal process — it must be findable by external security researchers and published in English.
The policy must include: a contact point for reporting security vulnerabilities, an acknowledgement timeline (best practice is within 72 hours), a commitment to keep reporters informed about the remediation process, and a statement about whether the manufacturer follows coordinated vulnerability disclosure (CVD) principles. The OPSS has published guidance recommending alignment with ISO/IEC 29147, the international standard for vulnerability disclosure [OPSS, 2024].
Critically, the policy must also state what the manufacturer will and will not do with reported vulnerabilities — for example, whether they operate a bug bounty programme or intend to patch older firmware versions.
3. Security Update Periods: Transparency at Point of Sale
Manufacturers must tell consumers, at the point of sale, the minimum period for which the product will receive security updates. This information must appear on the product, its packaging, or a document supplied with it — and must be accessible online too.
"At the point of sale" has been interpreted broadly by the OPSS to include online retailer product listings. A product listed on a UK e-commerce platform must display its minimum support period on that listing page. The period can be stated as a number of years (e.g. "minimum 5 years of security updates from date of purchase") or as a specific end date. Stating "no security updates will be provided" is legally permissible but commercially damaging — consumers must still be informed.
Who Must Comply: Manufacturers, Importers, and Distributors
The PSTI Act allocates distinct obligations to each tier of the supply chain. Understanding which role applies to your business is the starting point for any compliance programme.
| Role | Key obligations | Documentation required |
|---|---|---|
| Manufacturer | Implement all 3 security requirements; issue a Statement of Compliance; investigate complaints | Statement of Compliance; technical file; vulnerability disclosure policy URL |
| Importer | Verify the manufacturer has complied; attach importer's UK address to the product; report non-compliant products to OPSS | Copy of manufacturer's Statement of Compliance; records of due diligence checks |
| Distributor | Verify the manufacturer and importer have met their obligations before making products available | Records confirming compliance verification |
A single business may occupy more than one role. A UK company that designs products overseas and sells them in the UK under its own brand acts simultaneously as manufacturer and importer under the Act. The OPSS has made clear that supply chain complexity does not dilute individual obligations.
Businesses that discover a non-compliant product already on the market must notify the OPSS and take corrective action, which may include product recall. The obligation to notify applies to all three supply chain roles — not just manufacturers.
For UK businesses supplying connected devices to business customers (B2B), the Act still applies if the end product is likely to be used domestically by consumers. The critical test is whether the product is a "consumer connectable product," not the nature of the direct customer relationship.
Enforcement and Penalties: What Non-Compliance Costs
The Office for Product Safety and Standards (OPSS) is the designated enforcement authority for the PSTI Act. Since the Act came into force in April 2024, the OPSS has published guidance, engaged with trade associations, and begun active market surveillance — purchasing products and testing them for compliance against the three requirements.
The enforcement toolkit available to the OPSS under the Act is substantial:
- Compliance notices: Requiring a business to take specific remedial steps within a defined timeframe
- Stop notices: Prohibiting a business from supplying or offering to supply a non-compliant product
- Recall notices: Requiring businesses to remove products from consumers and the market
- Monetary penalties: Up to £10 million or 4% of qualifying worldwide revenues (whichever is greater) for serious or persistent non-compliance; up to £20,000 per day for ongoing contraventions after a notice has been issued [PSTI Act 2022, s.35]
The OPSS has authority to enter premises, require production of documents, and seize non-compliant products. It also has powers to publicise enforcement actions — making non-compliance a reputational as well as a financial risk.
In 2026, the OPSS enforcement focus has shifted toward market surveillance of products purchased through online marketplaces and direct-to-consumer imports. IT consultants and electronics businesses operating in the UK market who source products from manufacturers in Asia or Eastern Europe face particular scrutiny, as these supply chains have shown the highest rates of non-compliance with the default password prohibition.
The NIS2 Directive, which applies to UK businesses operating in EU markets, creates a parallel compliance obligation for network and information systems. For companies managing both UK and EU market access, understanding the interaction between the PSTI Act and NIS2 requirements is essential for avoiding double exposure to regulatory penalties.
Step-by-Step Compliance Roadmap for Connected Device Businesses
Achieving compliance with the PSTI Act is a structured process. The following roadmap applies whether your business is a manufacturer, importer, or distributor.
Step 1 — Product scope assessment: Identify every connected product in your UK product range. Cross-reference against the Act's exclusions (medical devices, smart meters, laptops, etc.) to determine scope.
Step 2 — Password audit: Test every in-scope product for universal or predictable default passwords. Engage firmware development teams to implement per-device unique passwords or mandatory setup flows.
Step 3 — Vulnerability disclosure policy: Draft and publish a vulnerability disclosure policy in English. Assign an internal owner for the security contact inbox and define response timelines. Register the policy URL in your Statement of Compliance documentation.
Step 4 — Support period definition: Determine and document the minimum security update period for each product. Update packaging, product listings on UK retail platforms, and in-box documentation accordingly.
Step 5 — Statement of Compliance: Issue a Statement of Compliance for each in-scope product, referencing the relevant Statutory Instruments under the PSTI Act 2022.
Step 6 — Supply chain due diligence: For importers and distributors, request Statements of Compliance from all suppliers, conduct periodic spot-checks, and document your verification process.
Step 7 — Ongoing monitoring: Establish a process for monitoring emerging vulnerabilities in your products, receiving and acting on disclosed vulnerabilities, and issuing security updates within the committed support period.
Key takeaway: Compliance is not a one-time exercise. The PSTI Act creates ongoing obligations — particularly around vulnerability disclosure and security update delivery — that continue for the full stated support period of each product.
As UK businesses increasingly connect their operations to AI-driven systems, the cybersecurity risk landscape is evolving rapidly. Firms should consider how their connected device security posture intersects with broader AI cybersecurity threats that are now affecting critical infrastructure and commercial networks alike.
How the UK's Approach Compares to the EU Cyber Resilience Act
The UK PSTI Act and the EU Cyber Resilience Act (CRA), which began its transitional application in 2024 with full enforcement from December 2027, share the same foundational objective: eliminating insecure-by-default connected products from the market. Both draw on ETSI EN 303 645 as a technical baseline. However, the scope and obligations diverge in ways that matter for businesses operating across both markets.
The PSTI Act focuses on three specific, auditable requirements. The EU CRA takes a broader approach, requiring a full conformity assessment process, CE marking for digital elements, and mandatory reporting of actively exploited vulnerabilities to national authorities within 24 hours. The CRA also covers software products without hardware components — an area the PSTI Act does not address.
For manufacturers selling into both the UK and EU markets, the most efficient path is to achieve PSTI compliance first (it is narrower in scope), then layer the additional CRA requirements on top. The CRA's mandatory 24-hour incident notification requirement has no direct equivalent in the PSTI Act, making it the most significant additional obligation for dual-market businesses.
The UK government has indicated it will keep the PSTI Act under review and may expand its scope — potentially addressing standalone software and additional product categories as the EU CRA demonstrates its regulatory model in practice.
Frequently Asked Questions About the UK Smart Devices Security Act
Which products are covered by the UK Smart Devices Security Act? The Act covers consumer connectable products — any device that connects to the internet, a mobile network, or another device via wireless technology. This includes smart TVs, security cameras, baby monitors, routers, wearables, and smart home appliances. Laptops, desktop computers, medical devices, smart meters, and electric vehicle charging points are explicitly excluded.
When did the UK Smart Devices Security Act come into force? Part 1 of the Product Security and Telecommunications Infrastructure (PSTI) Act 2022 came into force on 29 April 2024. Products placed on the UK market after this date must meet all three mandatory security requirements.
What are the maximum fines for non-compliance with the PSTI Act? The Office for Product Safety and Standards (OPSS) can impose monetary penalties of up to £10 million or 4% of a business's qualifying worldwide revenues for the preceding year — whichever is greater. Ongoing contraventions after an enforcement notice can attract additional penalties of up to £20,000 per day.
Does the Act apply to businesses that import connected products into the UK? Yes. Importers carry independent legal obligations under the PSTI Act. A UK importer must verify that the manufacturer has complied with all three requirements, keep a copy of the manufacturer's Statement of Compliance, and attach their own UK address to the product. Assuming the overseas manufacturer has handled compliance is not a legally adequate response.
How long must manufacturers support connected products with security updates? The Act does not specify a minimum support period — it requires manufacturers to state whatever period they commit to, transparently, at the point of sale. However, the OPSS guidance and ETSI EN 303 645 recommend a support period that reflects the product's expected useful life. For most consumer electronics, industry best practice in 2026 is a minimum of five years from date of first sale.
Disclaimer: The information in this article is provided for general informational purposes only and does not constitute legal advice. Businesses should seek independent legal counsel for advice on their specific compliance obligations under the Product Security and Telecommunications Infrastructure Act 2022.