 Andrew Reynolds
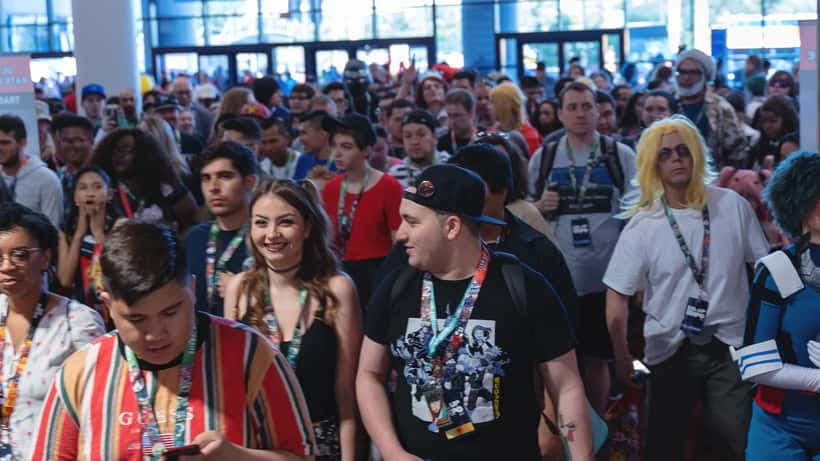
Australia's biggest gaming event is nine days away. From 9 to 11 October 2026, more than 85,000 attendees will pack the Melbourne Convention and Exhibition Centre for PAX Aus — three days of pre-release game demos, live tournaments, indie showcases, and hardware launches from over 500 exhibiting companies. SEGA is bringing four playable titles including Alien: Isolation 2 and Persona 4 Revival, Activision is previewing Call of Duty: Modern Warfare 4, and Square Enix will have multiple titles on the floor ahead of their global launches. By any measure, it is the largest concentration of Australian gamers in a single building all year — and IT security experts say that also makes it one of the most predictable cybersecurity exposure events on the national calendar.
PAX Aus 2026: What's at Stake on the Show Floor
PAX Aus has grown steadily since its Melbourne debut. Last year's edition drew 85,000 people across the three-day weekend, making it the second-largest gaming convention in the Southern Hemisphere. The 2026 edition adds more playable content than any previous year — over 90 titles spread across the Aus Indie Showcase, PAX Rising, and New Zealand's Centre of Digital Excellence booth, alongside hardware demonstrations from Aftershock PC, Mwave, and PowerA.
For most attendees, the experience is exactly what it looks like: an extraordinary few days of gaming with no consequences beyond sore thumbs and a lighter wallet at the merch store. But every demo station, every QR code, and every free WiFi access point on that floor represents a potential entry point for bad actors — and Australian gamers, as a group, are poorly prepared to recognise the difference between a legitimate network and a fraudulent one.
Research published ahead of PAX Aus 2026 by cybersecurity firm CyberFence found that fewer than three in ten Australians can reliably identify a spoofed public WiFi network. More concerning: 65.8 per cent of respondents said they would trust and connect to a network displaying the name of the venue they were attending, regardless of whether they could verify its legitimacy. At an event the size of PAX Aus, where the MCEC's official network coexists with networks managed by exhibitors, third-party vendors, and potentially bad actors, that level of exposure is significant.
The Four Attack Vectors IT Experts Are Watching at PAX Aus 2026
IT security specialists have identified four primary threat vectors relevant to large gaming conventions, each of which is present at PAX Aus in substantial form.
Evil twin WiFi is the most straightforward. An attacker sets up a portable access point broadcasting an SSID identical to — or plausibly similar to — the convention's legitimate network. "MCEC-Guest," "PAX-Official," or "PAX-Aus-Free" are all names that would attract automatic connections from attendees who connected earlier without scrutinising the network. Hardware capable of running this attack is available for under $50 AUD from consumer electronics retailers. Once a device connects, the attacker is in a position to intercept unencrypted traffic, redirect users to credential-harvesting login pages, and inject malicious content into web sessions.
Demo station keystroke logging is the threat most specific to gaming events. Demo stations at conventions run software installed by exhibitors on hardware managed by the venue. Without rigorous session isolation — which is rarely feasible at the pace of a three-day event — malware installed during one session can persist across multiple users. An attendee who logs into Steam, Epic Games, or PlayStation Network to access an existing save file or to enter a platform-linked competition is potentially exposing those credentials to every person who uses the same station after them.
QR code phishing has become endemic at conventions. PAX Aus 2026's show floor will be saturated with QR codes offering competition entries, discount codes, digital reward unlocks, and game keys. A fraudulent code placed over a legitimate one — or distributed via near-identical counterfeit signage — redirects the user to a convincing replica of a platform login page. According to the Australian Cyber Security Centre, QR phishing reports in Australia increased significantly through 2025, with conventions and sporting events identified as particularly high-risk environments.
Shoulder surfing and social engineering are lower-tech but highly effective in crowded environments. Password observation is straightforward in dense queues, and bad actors posing as event staff or fellow attendees can extract account credentials through seemingly helpful interactions.
What Happens When a PAX Aus Account Compromise Goes Undetected
The mechanics of a gaming account breach at a convention are worth understanding in concrete terms, because the timeline is unforgiving.
Take the case of a 26-year-old Sydney resident attending PAX Aus on Saturday 11 October. They hold a Steam library valued at approximately $1,100 AUD, a CS2 inventory with active market listings worth around $350, and a linked credit card with $500 in stored purchasing credit. On the show floor, they log into Steam at a publisher's demo station to load an existing save file for a preview title — a common and seemingly reasonable action. The station has been running since Thursday, has processed hundreds of logins, and has not been reimaged between sessions. A keylogger installed by a previous session records the login credential in under 30 seconds.
Within 20 minutes — roughly the time it takes to queue for the next demo — the attacker has logged in remotely, changed the account password, removed the linked mobile authenticator via Steam's support recovery process, and listed the CS2 inventory at 60 per cent market value for rapid liquidation. The original owner receives a mobile notification from the Steam app showing a new login from an unrecognised device in an offshore location.
From that notification to account lockout, the recovery window is between 15 and 45 minutes. If the email address linked to the account has also been compromised — attackers frequently target this first using credential-stuffing attacks from earlier breaches — the full recovery process with Steam Support takes between two and six weeks. The return of sold inventory is not guaranteed. Virtual item sales on Steam are final; there is no platform-enforced chargeback.
Total exposure in this scenario: up to $1,950 AUD in digital assets and stored credit. Partial recovery is possible only if the victim acts within the first 30 minutes and has a hardware-based backup authentication method not stored on the compromised device.
An IT security professional consulted before the event can audit account security configurations, implement hardware-key authentication across platforms, and identify credential reuse patterns that make this kind of cascade attack possible in the first place. For more on what Australian gamers face in the current cybersecurity environment, see our coverage of Metro 2039 and the gaming security risks Australian players face and the data privacy issues raised by GTA 6's Australian launch.
Five Steps to Take Before PAX Aus 2026 Opens Its Doors
The most effective PAX Aus security preparation happens in the week before the event — not during it, when the combination of queues, noise, and excitement makes security lapses far more likely.
Use mobile data, not convention WiFi. Australia's three major carriers provide adequate bandwidth for social media, messaging, and light browsing. If you need to check your platform accounts at the event, do it over 4G or 5G — never over an unverified network, regardless of how official its name appears.
Enable hardware-based two-factor authentication. Authenticator apps (Google Authenticator, Authy) are significantly stronger than SMS-based verification. FIDO2-compliant hardware security keys — available from approximately $65 AUD — are stronger still. Both Steam and Epic Games support hardware keys. If you have not configured either, do it now.
Create a convention-specific account for demo use. If you intend to log into a shared demo station, register a throwaway account with no linked payment method, no valuable inventory, and no connection to your primary account. Never use your main account on hardware you do not control.
Strip stored payment methods before you go. Removing credit card details from your platform accounts before 9 October eliminates one of the two primary financial exposure routes. The brief inconvenience of re-entering card details after the event is significantly preferable to a fraudulent charge dispute.
Book an IT security consultation before the convention. A one-hour session with an IT security professional — available through ExpertZoom without leaving home — can identify credential reuse across platforms, misconfigured privacy settings, and authentication weaknesses that are invisible to most users. For 85,000 Australians spending up to $1,900 AUD in digital assets at a three-day event, an hour of professional preparation is a reasonable investment.
PAX Aus 2026 is going to be an exceptional event. The games on the floor are genuinely exciting, the community is strong, and Melbourne in October is a good place to be. It is also, for approximately 72 hours, one of the most target-rich environments for cybercriminals in Australia. Go prepared.
